
A secure network is built from several layers that each stop a different kind of attack. No single product does everything. This guide explains the core network security components, firewalls and intrusion detection, encryption, endpoint security, SIEM monitoring and patch management, and how they work together.
Key takeaways
- Firewalls and intrusion detection control and inspect traffic at the edge.
- Encryption protects data in transit and at rest.
- Endpoint security protects every device on the network.
- SIEM monitoring and patch management keep defences up to date and visible.
Firewalls and intrusion detection systems
A firewall allows or blocks traffic according to rules, separating trusted networks from untrusted ones. An intrusion detection system (IDS) watches traffic for suspicious patterns, and an intrusion prevention system (IPS) can block them automatically. Together they form the first line of defence.
Encryption
Encryption encodes data so only authorised parties can read it. Use it for data in transit, such as VPNs and HTTPS, and for data at rest on servers, laptops and backups. If data is stolen, encryption makes it far less useful to the attacker.
Endpoint security
Every laptop, server, phone and connected device is a possible entry point. Endpoint protection and endpoint detection and response (EDR) tools stop malware, detect unusual behaviour and help isolate a device if it is compromised. In industrial sites this includes cameras, weighbridge PCs and gate systems.
SIEM monitoring
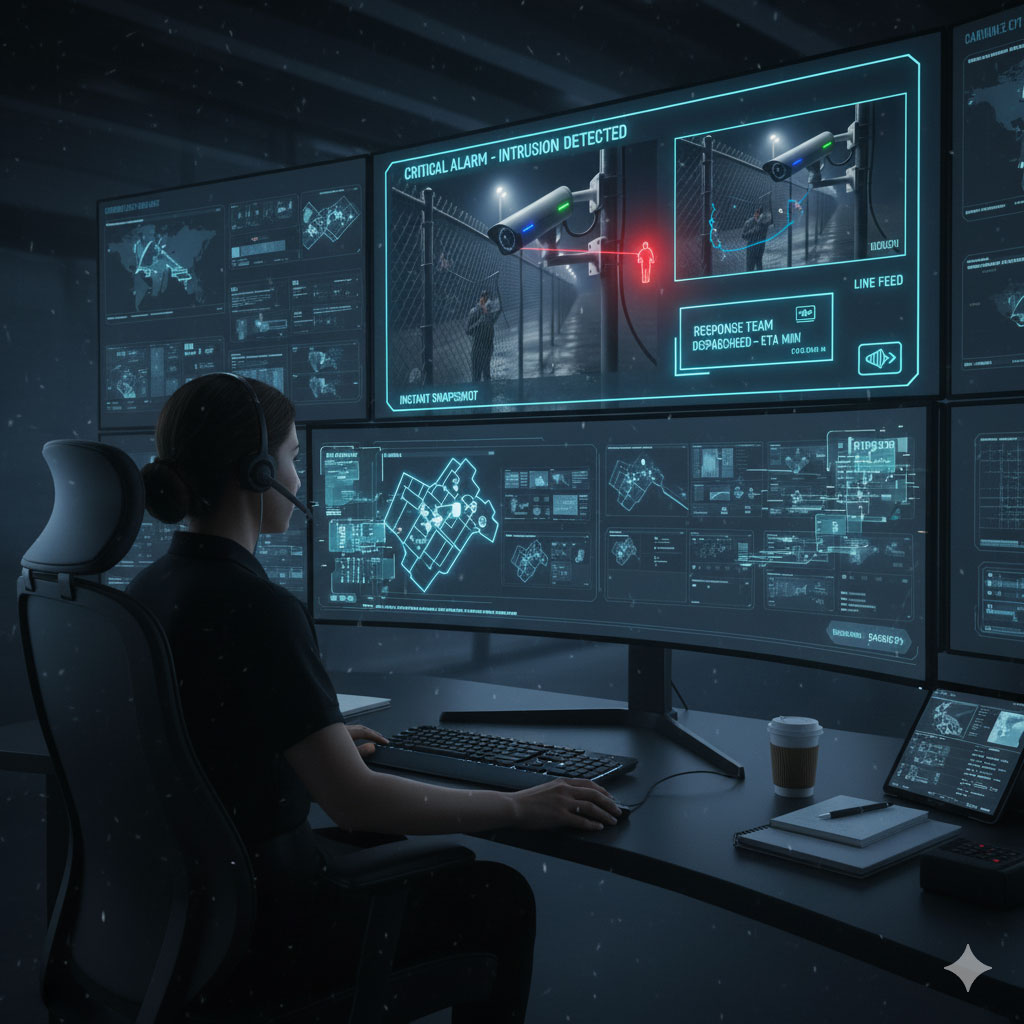
Security information and event management (SIEM) collects logs and alerts from firewalls, servers, endpoints and applications, correlates them and highlights real threats. A monitoring team can then investigate and respond quickly instead of searching through separate systems.
Patch management and keeping up with threats
| Component | Protects against |
|---|---|
| Firewall and IDS/IPS | Unauthorised access, network attacks |
| Encryption | Data theft and interception |
| Endpoint security | Malware, ransomware, compromised devices |
| SIEM monitoring | Undetected attacks, slow response |
| Patch management | Known software vulnerabilities |
Attackers often exploit known weaknesses that already have a fix. Regular patching of operating systems, applications and device firmware closes those gaps. As IoT devices multiply, keeping an inventory of every connected device becomes part of the job.
For the layered view, read what a cyber security network is and cybersecurity solutions for businesses. Suraj Informatics offers cyber security network and monitoring services.
Network security components: common questions
What are the main components of network security?
Firewalls, intrusion detection and prevention, encryption, endpoint security, SIEM monitoring and patch management.
What is the difference between IDS and IPS?
An IDS detects and alerts on suspicious traffic; an IPS can also block it automatically.
Why is SIEM important?
It brings security data from many systems into one place so threats are spotted and handled faster.
How often should systems be patched?
As soon as practical after security updates are released, following a regular, tested schedule.
Talk to our cyber security team
Tell us about your network and systems, and we will suggest the right protection and monitoring.